

Copilot Studio, Claude, ChatGPT and Gemini now act inside your enterprise, with access to your data and applications. Kanopy Security shows you what they can reach, watches what they actually do, and stops what they shouldn't.

The Creatures In The Shadows
From quiet misconfigurations to risky behavior, here’s what’s prowling in your AI workforce.

Unmapped skills, agents and tasks
Every skill, agent and task people hand to AI, with no inventory behind it.

Uncharted data access
MCP servers are how agents touch enterprise data. Few teams know which ones are in use, approved or not, internal or external.

Exposed knowledge and hard-coded secrets
Keys and tokens embedded in skills and MCP servers. Sensitive personal and business data exposed as knowledge.

Overprivileged agents
Connected to more than the task needs. Built to summarize, able to send email.

Data leakage
Outputs, connectors and tool calls that carry enterprise data to external services.

Malicious activity
Rogue agents, untrusted skills and prompt injection: instructions hidden in text, carried out with the agent’s permissions.

Accidental activity
Agents that delete, overwrite or overshare because an instruction was vague or a permission was too broad.
The Jungle Awaits
Welcome to the wild frontier of agents, skills and MCP servers built by your citizen developers. When visibility drops, risky automations spread fast. We don’t just hack at vines. We hand you the machete and the map to secure your AI workforce.


Trusted by Fortune 500 Companies

“Our security architects started seeing more & more no-code solutions. We already have a strong traditional AppSec program. But LCNC was clearly a gap in our knowledge.”

“We needed a way to implement security and governance controls to safeguard and ensure the success of our large-scale automation initiative.”

“Before Kanopy, we didn't have a clue what security impact the automation activities created.”

“Kanopy solves the exact problem I was looking to solve, securely enabling citizen developers.”
Why Kanopy
Agentless
No endpoints. Nothing to install. Live from day one.
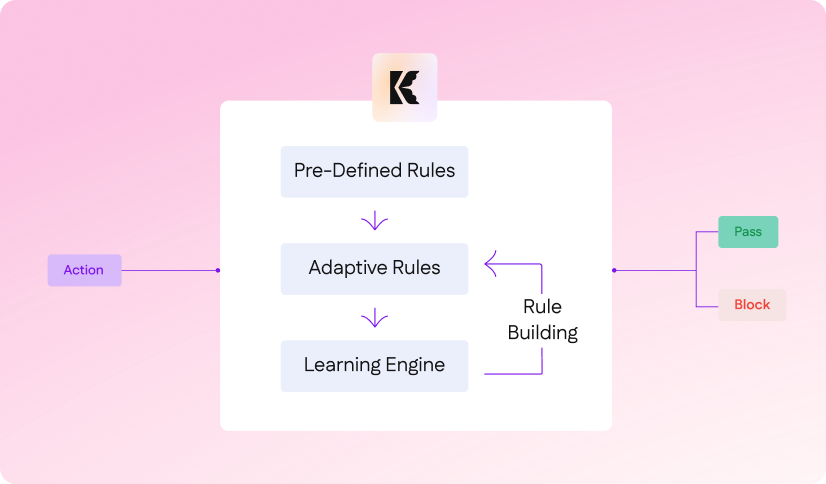
Build-time to runtime
Security across the whole life of every agent, skill and app.
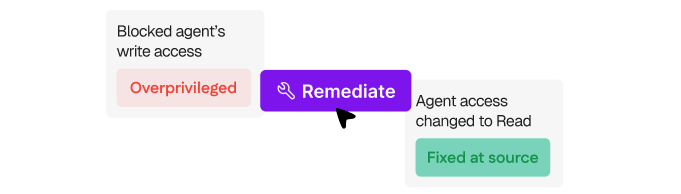
Auto-remediation, shifted left
Quick-fix action buttons and guidance tailored to end users to remediate risks.
One control plane
Every agent, app and automation, across every platform, in one place.
With Kanopy You Can

See
it all
Every agent, skill and MCP server, mapped across every enterprise AI tool. So you can manage AI exposure from one place.

Fix
it fast
One-click remediation for business users, detailed insights for security teams.

Watch it
run
Dynamic and runtime analysis shows what agents actually do, not just how they were configured.

Stop it
early
Block prompt injection and destructive or malicious activity at execution time.